Turn AI governance requirements into a structured internal review. Assess, identify gaps, prioritize actions, and move forward with greater clarity.
ISO/IEC 42001:2023 AI Internal Assessment Checklist · by Ravi Rajput
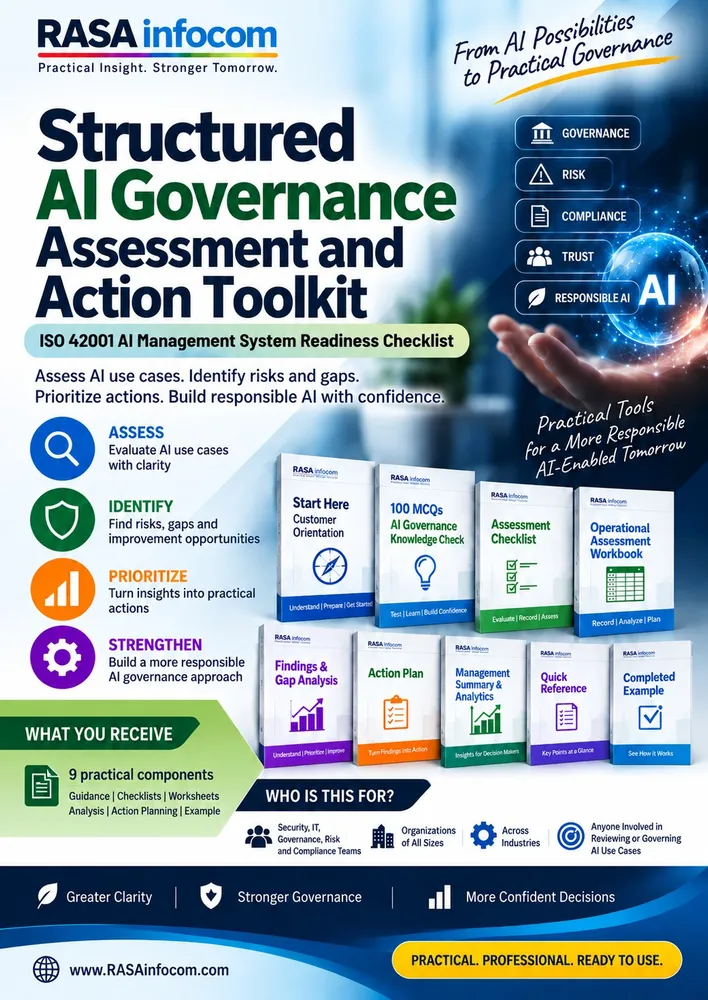
The ISO 42001 AI Internal Assessment Checklist is a practical working tool for organizations that want to review their AI management system position in a structured way and turn observations into practical next actions. Built around ISO/IEC 42001, the assessment covers 65 structured coverage units across the standard's Clauses 4 to 10 and Annex A controls. It helps teams work through relevant areas, record evidence and context, identify gaps or uncertainties, assign priorities, and organize improvement actions. The package includes a customer guide, detailed assessment checklist, findings and gap analysis, action plan, quick reference, completed example, and an operational XLSX workbook with management-oriented analytics. Designed for security, IT, governance, risk and compliance teams, it can support organizations of different sizes and across industries.
- BUY → PAY → READ
- 7-day refund window on faulty or wrongly-charged orders — see Refund Policy.
- Secure checkout via Razorpay.
This product includes 8 files
- 01_Initial_Customer-GuideWord
- 02_Assessment-Checklist_65-UnitsWord
- 03_Findings-Gap-AnalysisWord
- 04_Action-PlanWord
- 05_Quick-ReferenceWord
- 06_Customer-Value-BriefWord
- 07_Sample-Completed-ExampleWord
- ISO 42001-OPERATIONALASSESSMENT-WorkbookSpreadsheet
What you get
Everything inside, at a glance
65 structured ISO/IEC 42001 coverage units for systematic internal review
Coverage spanning Clauses 4 to 10 and applicable Annex A control areas
Practical assessment guidance that helps teams work through the subject systematically
Evidence and contextual-information recording to support documented assessment work
Applicability handling so relevant areas can be considered in organizational context
Structured findings and gap analysis to capture issues, uncertainties and improvement needs
Priority handling to help teams distinguish areas requiring greater attention
Action planning with ownership and target or review dates
Operational XLSX workbook for assessment, findings, actions and management-oriented review
Customer DOCX guide and supporting documents for preparation, assessment and follow-through
Completed example using fictional illustrative information to demonstrate the working approach
Designed for repeat assessment, review and comparison of progress over time
**8-file professional assessment toolkit | DOCX + XLSX | Instant digital access**
What it is
AI governance becomes difficult when teams know they need to review their practices but do not have a clear working structure for doing it. ISO/IEC 42001 provides a foundation for an AI management system, but organizations still need a practical way to examine their current position, capture what they know, identify areas requiring attention, and organize the work that follows.
The ISO 42001 AI Internal Assessment Checklist is designed for that working stage. It provides a structured internal assessment that helps teams move from broad requirements to organized review and improvement activity.
The assessment covers 65 coverage units across ISO/IEC 42001 Clauses 4 to 10 and Annex A. The content addresses areas such as organizational context, leadership and planning, AI management system processes, resources and operational considerations, performance evaluation and improvement, together with the applicable Annex A control areas.
The working journey is straightforward:
Understand → Assess → Record → Analyse → Act → Review
Teams can record responses, applicability, evidence and contextual information while working through the assessment. Findings and gaps can then be captured separately, with priority, ownership and target or review dates used to turn observations into an organized action plan.
The package includes a DOCX assessment guide and supporting customer documents, together with an operational XLSX workbook. The workbook provides structured assessment recording, status and priority handling, findings, action planning, and management-oriented summary analytics. This makes it possible to use the product as a working assessment rather than simply reading through a checklist.
It is suitable for security, IT, governance, risk and compliance teams, as well as cross-functional teams involved in AI governance and management-system activities. The assessment can be used for an existing AI management system, preparation activities, internal review, improvement planning, or repeat assessment over time.
The product is deliberately practical rather than theoretical. It helps teams start with an organized assessment structure instead of building one from a blank document, while leaving organizational decisions and professional judgement with the customer.
The assessment uses completion and status information together with priority handling. These indicators are intended to organize the assessment workflow and resulting actions. They are not presented as certification, conformity, regulatory, safety or numerical compliance scores.
The product supports internal assessment and decision-making, but it is not a formal audit, certification, legal opinion, regulatory approval or professional assurance service. Applicable requirements should also be considered in the relevant organizational and jurisdictional context.
For organizations building a more disciplined approach to AI management-system review, this toolkit provides a practical starting point for understanding the current position, documenting observations and turning identified needs into a manageable improvement programme.
Who wrote this
Ravi Rajput
Ravi Rajput is an independent technology professional and advisor with more than 25 years of experience across Information Technology, Information Security, Operational Technology and manufacturing IT systems. His professional work includes cybersecurity, digital transformation, governance, risk, compliance and ISO-related technology environments. He brings a practical perspective shaped by working across technology and operational environments where governance needs to connect with real-world implementation. His broader professional interests include responsible use of technology, knowledge sharing and practical communication of complex technology subjects. His publications cover areas including cybersecurity, AI, compliance and technology. This experience informs a practical approach to AI governance that connects assessment, evidence, organizational context and improvement actions.
Reviews
What buyers are saying
No reviews yet — be the first to leave one.
Questions
Turn AI governance requirements into a structured internal review. Assess, identify gaps, prioritize actions, and move forward with greater clarity.
Keep going
You might also like
by Ravi Rajput
₹49
by Ravi Rajput
₹599