Security Audits · Secure Infrastructure · DevSecOps Advisory
We secure the infrastructure your business runs on.
RASA Infocom audits, builds, and advises on infrastructure security for engineering teams who'd rather find the gaps themselves than have an attacker find them first.
What we do
Services built around real risk, not checkbox compliance
Security Audits
A structured review of your infrastructure, code, and processes that tells you exactly where you're exposed, ranked by what to fix first.
Secure Infrastructure Builds
We design and stand up cloud infrastructure with security built into the architecture, not bolted on after an incident.
DevSecOps Advisory
Ongoing advisory to help engineering teams bake security into their existing workflow instead of treating it as a separate step.
Knowledge products
Built from the same playbook we audit with
Digital Edition
ISO/IEC 42001:2023 AI Internal Assessment Checklist
by Ravi Rajput
The ISO 42001 AI Internal Assessment Checklist is a practical working tool for organizations that want to review their AI management system position in a structured way and turn observations into practical next actions. Built around ISO/IEC 42001, the assessment covers 65 structured coverage units across the standard's Clauses 4 to 10 and Annex A controls. It helps teams work through relevant areas, record evidence and context, identify gaps or uncertainties, assign priorities, and organize improvement actions. The package includes a customer guide, detailed assessment checklist, findings and gap analysis, action plan, quick reference, completed example, and an operational XLSX workbook with management-oriented analytics. Designed for security, IT, governance, risk and compliance teams, it can support organizations of different sizes and across industries.
₹999
Digital Edition
Cyber Smart Playbook
by Ravi Rajput
Cyber Smart Playbook is a practical, jargon-free digital guide built around 250 cybersecurity habits for everyday digital life. It helps people make safer decisions across work, home, family, passwords, email, mobile devices, digital payments, social media, AI tools and situations where something suspicious or harmful happens. The playbook is designed for everyday users and does not require a cybersecurity or technical background. It can be read from beginning to end, used as a practical reference, or opened directly at the habit relevant to a particular situation. Written by Ravi Rajput, a technology leader with 25+ years of experience across Information Technology, Information Security and Digital Transformation, the playbook translates professional experience into practical guidance that is easy to understand and apply. It is available as an instant digital edition containing the CyberSmart-Playbook PDF.
₹49
Digital Edition
Small Business Cybersecurity Readiness & Action Planner
by Abhay Rajput
The Small Business Cybersecurity Readiness & Action Planner is a practical self-assessment tool for small businesses and small organizations that want a clearer view of their current cybersecurity readiness and a more organized way to improve it. It is designed around the NIST Cybersecurity Framework 2.0 and helps users review important areas of cybersecurity, record their current position, identify gaps and priorities, and turn findings into practical next actions. The product combines a customer guide with an interactive XLSX assessment workbook and dashboard capability. It supports repeat assessment and can be used by owners, managers, operations leaders, IT and security personnel, and consultants supporting smaller organizations. The result is not simply a completed checklist, but a structured starting point for understanding strengths, recognizing areas needing attention and organizing an improvement plan.
₹299
Digital Edition
ISO 42001 AI Management System Gap Assessment
by Ravi Rajput
The ISO 42001 AI Management System Gap Assessment is a practical assessment and improvement-planning resource for security, IT, governance, risk and compliance teams that need a structured view of their current AI management-system position. It helps organizations examine relevant arrangements, record supporting evidence, identify gaps and organize practical improvement actions against ISO/IEC 42001.
The assessment is designed around controlled coverage of Clause 4 to Clause 10 requirements and relevant Annex A reference controls, with status, priority, evidence and action treatment. The customer package includes guidance, an operational XLSX workbook, assessment results, gap and action tracking, dashboard and management reporting support, reference material and a fictional completed example.
It is designed for cross-industry use and can support reassessment and management review. It is not a certification, formal audit determination, legal opinion or guarantee of compliance.
₹599
Digital Edition
AI Use-Case Governance Assessment | Practical AI Governance Toolkit
by Abhay Rajput
The AI Use-Case Governance Assessment is a practical working toolkit for organizations that need a structured way to review an AI use case or proposed AI use case. Designed for security, IT, governance, risk and compliance teams, it brings together 64 assessment items across 16 governance domains. The assessment helps teams examine governance considerations, record responses and evidence, identify gaps and uncertainties, prioritize findings, and organize improvement actions with ownership and target or review dates. The package includes a DOCX Assessment Guide and an operational XLSX Workbook with assessment progress, status tracking, a consolidated Action Plan and a fictional completed example. It is designed to support informed organizational discussion and decision-making without presenting itself as a certification, audit or compliance determination.
₹299
Digital Edition
ISO 27001 Readiness Checklist
by Ravi Rajput
The ISO 27001 Readiness Checklist is a practical working assessment for organizations that want a structured way to review information security readiness, identify gaps and organize improvement actions. It covers 126 structured coverage units across ISO/IEC 27001:2022 Clauses 4 to 10 and the separate Annex A control population. The package provides assessment guidance, structured status and priority recording, evidence capture, findings and gap identification, action planning, ownership and review tracking, together with management-oriented output. The assessment can help security, IT, governance, risk and compliance teams create a clearer picture of their current position and decide what deserves attention next. It is designed as a practical assessment and decision-support tool, not as a certification, formal audit determination or guarantee of compliance.
₹999
Digital Edition
India DPDP Gap Assessment and Action Planning
by Ravi Rajput
India DPDP Gap Assessment and Action Planning is a practical working tool for organizations that need to understand differences between their current state and the intended Digital Personal Data Protection framework/law state. Designed for privacy, compliance, legal and data-governance teams across industries and organization sizes, it helps users assess their position, capture supporting evidence, identify gaps, prioritize improvement needs and organize actions. The product combines operational assessment with gap analysis, status and priority tracking, action planning, evidence capture, dashboard views, quick-reference guidance and a management summary. Delivered through DOCX and XLSX components within a customer-ready package, it supports a structured journey from assessment to interpretation and practical improvement planning. Its currentness-sensitive approach requires verification of applicable official requirements and guidance in the relevant organizational context.
₹599
Digital Edition
Structured AI Governance Assessment and Action Toolkit
by Ravi Rajput
The AI Use-Case Governance Assessment is a practical working tool for security, IT, governance, risk and compliance teams that need a structured way to review an AI use case and turn observations into practical next actions. Designed for cross-industry use, it helps teams consider governance and accountability, risk, responsible AI, data, human oversight, security, transparency, impact, legal and regulatory context, controls, evidence, residual issues and improvement actions. The product provides a structured assessment guide and operational workbook, with support for recording context and evidence, identifying findings and gaps, setting priorities, assigning owners, tracking target or review dates, and reviewing progress. It is designed to provide a clearer view of the current governance situation and help teams organize improvement work without starting from a blank document.
₹599
Digital Edition
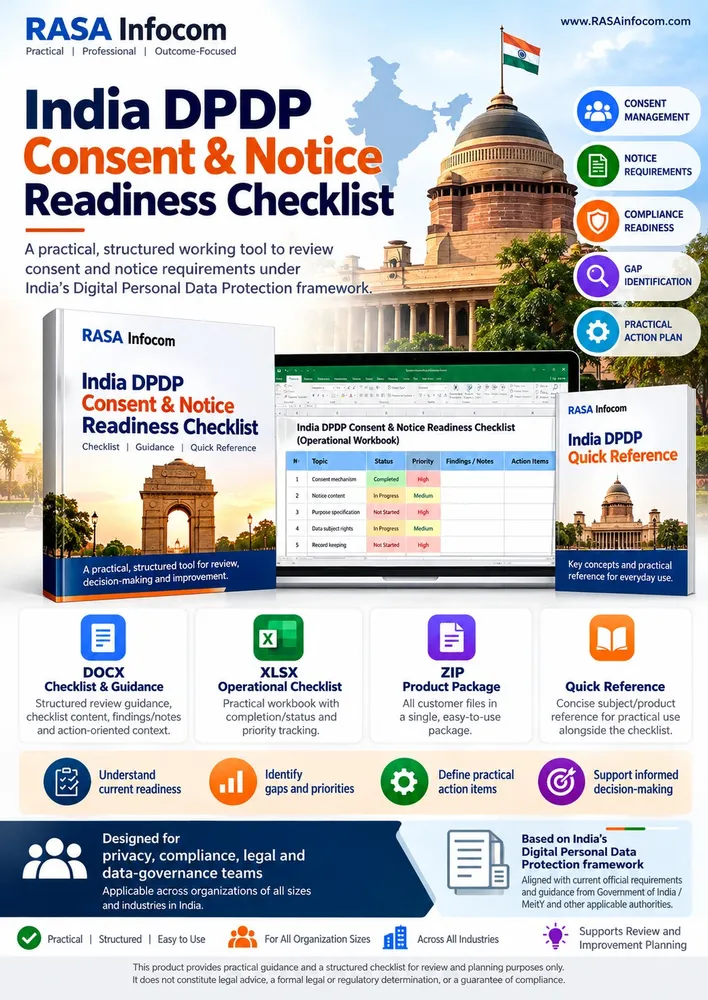
India DPDP Consent & Notice Readiness Checklist
by Ravi Rajput
The India DPDP Consent & Notice Readiness Checklist is a practical
working tool for privacy, compliance, legal and data-governance teams
that need a structured way to review consent and notice readiness.
Designed for organizations of all sizes and across industries in India,
it helps teams prepare for review, work through relevant checklist
areas, record findings and notes, identify priorities, and organize
practical action items.
The product is built around the Digital Personal
Data Protection framework and is intended to be used with current
official requirements and guidance from Government of India, MeitY and
other applicable authorities.
Customers receive a structured checklist
and guidance in DOCX, an operational XLSX checklist for recording status
and priorities, a Quick Reference, and the complete product package in
ZIP format.
It supports practical review and improvement without
presenting the checklist as legal advice or a formal determination of
compliance.
₹599
Digital Edition
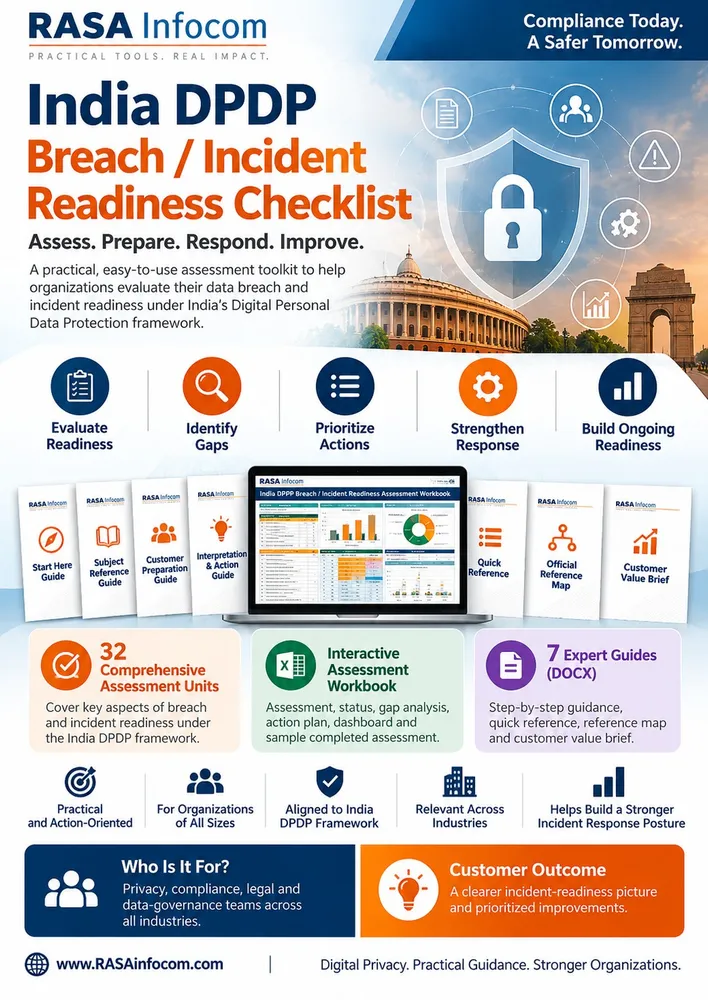
India DPDP Breach & Incident Readiness Assessment Checklist
by Ravi Rajput
The India DPDP Breach & Incident Readiness Assessment Checklist is a practical working tool for privacy, compliance, legal and data-governance teams that need to review how prepared their organization is to identify, assess, escalate and respond to personal data breach situations.
It helps teams examine incident-readiness arrangements, record evidence and findings, identify weaknesses, prioritize improvement needs and organize practical actions. The product is designed around a clear journey from assessment to findings, priority actions and an improvement plan.
It includes customer-facing guidance in DOCX and an operational XLSX workbook with assessment, status and priority tracking, gap and action management, dashboard-oriented reporting and quick-reference support. Designed for organizations of all sizes, it provides a structured starting point for reviewing readiness without presenting itself as legal advice or a formal regulatory determination.
₹599
Not sure where to start?
Tell us what you're building and we'll tell you honestly whether we're the right fit.
Get in touch